← Agenda / WED 23 / The Things Forum Two‹ Prev sessionNext session ›
PanelSecurity & ComplianceSecurity
SBoM and vulnerability requirements for the CRA
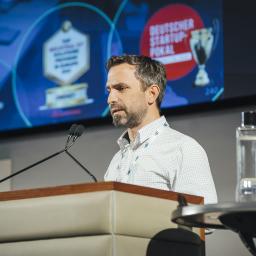
WATCH THE TALK · AMSTERDAM 202624:14
Software Bills of Materials (SBOMs) and effective vulnerability management are central to demonstrating compliance with the Cyber Resilience Act (CRA). This panel will explore the practical challenges of creating and maintaining SBOMs, managing vulnerabilities throughout a product's lifecycle, and meeting the CRA's expectations for transparency and ongoing security. Join industry experts as they discuss best practices, implementation strategies, and lessons learned from early compliance efforts.